By: James Vance – SeaPRwire – Most industrial connectivity projects start with the wrong question. Teams ask how fast the 5G radio is. They count Ethernet ports. They ignore the serial devices still running the plant and the cellular links that drop without warning. That mismatch is the real friction.
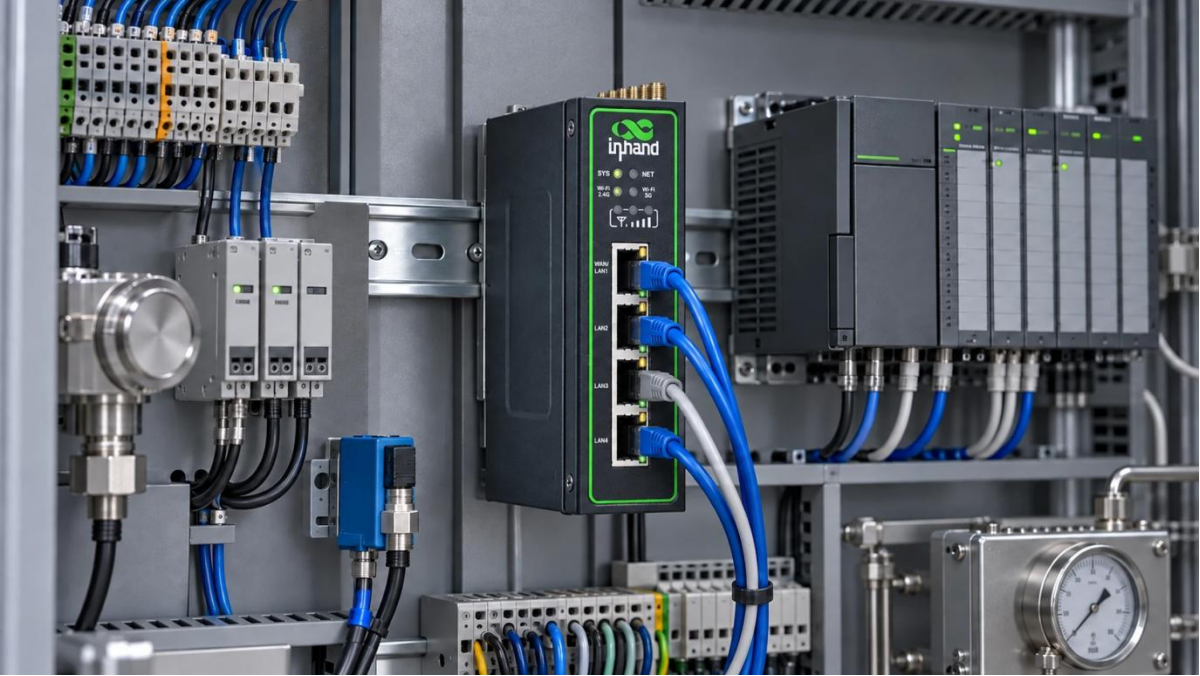
InHand Networks put the IR624 forward as a working example of how to close those gaps. The router is not presented as a universal fix. It is a concrete reference for five practical layers that decide whether field gear actually stays online and usable.
Start with the interfaces the plant already owns. Sites mix PLCs, meters, controllers and sensors from different decades. Some speak Ethernet. Others still run RS-232, RS-485 or Modbus RTU. Swapping every box just to reach the cloud adds cost and risk. The IR624 keeps those assets in place. It carries four Gigabit Ethernet ports, one RS-232 port and one RS-485 port. It supports TCP and UDP transparent transmission plus a Modbus RTU-to-TCP bridge. The design question is not whether the ports exist. It is whether the full data path has been tested with the real devices and the upstream application that will consume the data.
Cellular access is the next layer, and it is not the same as service continuity. 5G can deliver higher bandwidth and lower latency than older generations. Industrial sites still face variable signal, coverage holes, SIM problems, handovers, interference and upstream outages. For unattended locations the router must detect a failed or degraded path and execute a defined recovery. Dual-SIM failover, cellular-to-wired backup, heartbeat detection with automatic redial and an embedded watchdog are the tools listed for the IR624. These mechanisms improve resilience. They do not guarantee uninterrupted service. Recovery thresholds and failover behavior still need testing against the application’s tolerance for delay and packet loss.
Remote access has to be bounded before the first unit ships. Once operational equipment sits on a wide-area link, exposure changes. Engineers, cloud services and supervisory systems may need entry, yet only the required users, services and traffic flows should be allowed. The IR624 supplies firewall filtering, access-control lists, policy-based routing, 802.1X and VPN options that include IPsec, L2TP, OpenVPN and WireGuard. Those features form a toolbox, not a finished security architecture. The organization still owns the risk assessment, the segmentation model and the policies that decide what is permitted.
Fleet operations demand more than a successful pilot. A configuration process that works for one router rarely scales to dozens or hundreds of sites. Consistent configuration, status visibility, alerts, logs, firmware control and repeatable troubleshooting become mandatory. The IR624 can link to InHand DeviceLive for remote and batch management. Cloud management is not a convenience add-on. It is part of the operating model for distributed infrastructure. Its value appears only when monitoring, change control and incident response are already embedded in existing processes.
Physical and lifecycle realities close the list. Network functions matter only if the hardware survives the installation environment. Input power, grounding, temperature, humidity, vibration, electromagnetic compatibility, enclosure protection, antenna placement and mounting space all need evaluation. The IR624 uses a fanless metal case, DIN-rail mounting and a 9-to-48 VDC input. Published ratings include IP30 protection and operating-temperature options that vary by configuration. IP30 offers no outdoor weather protection, so exposed sites require an additional enclosure and a site-specific environmental review. Carrier compatibility, regional certifications, firmware policy, spare units and the service life of connected equipment also shape whether a pilot can move into sustained production.
These five layers form a single path from field device to cloud. Field devices connect through Ethernet or serial interfaces. Edge adaptation moves selected legacy data into IP systems via transparent transmission or protocol conversion. Wide-area access supplies cellular and wired links plus SIM strategy and failover rules. Secure connection limits and protects traffic with VPNs, firewalls, access controls, routing and authentication. Operations covers monitoring, alerts, logs, configuration and firmware across the installed base. Viewing the system this way clarifies responsibility boundaries and test points. It also stops teams from treating the router as an isolated box whose behavior somehow leaves field equipment, carrier services, security controls and business applications untouched.
Before any industrial 5G router is selected or deployed, five concrete questions remain useful. Which physical interfaces and protocols does the installed equipment actually use? What outage duration can the application tolerate, and how will failover be tested? Which users and services require remote access, and what traffic must be denied? How will configurations, firmware, alerts and logs be managed across the entire fleet? Does the chosen hardware match the site’s power, temperature, enclosure and compliance requirements? Those questions move the conversation from feature checklists to end-to-end engineering review. A device such as the IR624 can combine several of the required functions in one unit. Successful deployment still rests on system design, validation and operational discipline.
The practical takeaway is straightforward. Treat the router as one component inside a larger, tested path rather than as the solution itself. Validate every interface, recovery rule and management process against the real plant and the real application. That is the only way the link stays useful after the pilot ends.
Author bio: James Vance, senior commentator for international technology weeklies who has covered industrial networking and edge systems for more than fifteen years.
source https://newsroom.seaprwire.com/press-releases/technologies/the-router-isnt-the-hard-part-why-industrial-5g-still-trips-on-legacy-gear-and-silent-failovers/